Binance Reopens 87 Networks After $6.3B Crypto Hack
Binance restored withdrawals on 87 networks after its $6.3 billion hack. Its November 14 update sets a new deadline, but some withdrawal routes remain closed.
Kava Lend lost 55.2 million KAVA in a November 14 exploit. An old BUSD market inflated collateral 243,000 times, exposing lenders and forcing transfer pauses.

By Mikko Mikailov4 min read
Kava Lend, the lending protocol on the Kava blockchain, was exploited on November 14, 2026, when two linked wallets borrowed 55.2 million KAVA through a distorted BUSD collateral market. The tokens were valued at $3.76 million at pre-attack prices, according to The Block. The attackers converted a substantial share into other assets, while Kava reported that the incident remained confined to its lending application. The protocol has not published a final loss assessment or a reimbursement plan as of November 15.
The entry point was not a new token or a breached private key. It was a BUSD lending market that had little cash left in it. BUSD's issuer, Paxos, stopped issuing new tokens in February 2023, yet Kava Lend's old market remained part of the protocol's accounting system.
Bitquery's November 14 blockchain reconstruction identified a problem in the calculation that credits interest to depositors. Kava Lend divided accrued interest by the effective amount supplied to a market. Its code checked for a supply figure of exactly zero but did not adequately handle a positive figure approaching zero. The attackers adjusted the BUSD pool to just two minimum accounting units of effective supply.
Within three minutes, the pool's supply interest index rose from 2.76 to 671,187. A deposit worth only thousands of BUSD was then recorded as a claim of 1.26 billion BUSD. No equivalent amount of real collateral entered the protocol. The number existed in its books.
That faulty claim supported a repeating sequence of loans and liquidations. One wallet borrowed KAVA, while another liquidated the loan and cleared its debt. According to Bitquery, the liquidation process seized practically no BUSD because the collateral had already been withdrawn. Each closed loan reopened capacity under the borrowing cap.
The two-wallet operation ran from 04:04 to 05:42 UTC on November 14, completing 127 borrowing rounds. Bitquery also traced smaller tests involving the BUSD market between November 8 and 10. The available record establishes preparation, but not the identities of those controlling the wallets.
The financial figures describe different stages of the incident. Treating the value of all borrowed tokens as the amount converted into cash would overstate the attackers' realized proceeds.
| Measure | Recorded figure | Basis |
|---|---|---|
| KAVA borrowed through the exploit | 55,205,051 KAVA | Bitquery, November 14 |
| KAVA retained after other borrowers' loans were repaid | 53.9 million KAVA | Bitquery, November 14 |
| Value of drained tokens before the market reaction | $3.76 million | The Block, November 14 |
| KAVA transferred to BNB Chain | 49.2 million KAVA | Bitquery, November 14 |
| Proceeds from the BNB Chain sale | $2.09 million | Bitquery, November 14 |
| USDT transfer blocked by Relay | 612,416 USDT | Bitquery, November 14 |
The attackers moved the bulk of the tokens from Kava to BNB Chain through LayerZero. Bitquery traced the sale of 48.4 million KAVA in 35 minutes, followed by transfers through cross-chain services. The sale itself depressed the market price, which explains the gap between the pre-attack token valuation and the proceeds received.
The money did not stay in one wallet. Bitquery traced $1.17 million in USDC deposits to eight Hyperliquid accounts, where the funds were exchanged for a token called XMR1. A separate route reached Solana. These are transaction observations, not evidence of who owns the destination accounts.
The Relay bridge recorded an attempted transfer of 612,416 USDT as failed with the reason BLOCKED_WALLET. Its records showed no corresponding ETH payout when Bitquery checked on November 14. That is a blocked transfer, not confirmed restitution. Bitquery also noted that the deposit was marked as potentially withdrawable by the sender, leaving its ultimate disposition unresolved.
In its November 14 statement, Kava said the activity was isolated to Kava Lend and was not an infinite mint. The distinction is material. The attackers did not generate new KAVA through a supply bug. They removed tokens that depositors had placed in a lending pool.
The Kava team said partner exchanges paused KAVA deposits and withdrawals as a precaution. Kava also suspended withdrawals through the Axelar bridge. The stolen tokens had crossed to BNB Chain through LayerZero instead, so the Axelar suspension was a separate containment measure. Upbit also issued a trading caution on November 14. Restrictions on transfers do not, by themselves, mean spot trading stopped.
The immediate exposure differs by where tokens were kept. A KAVA holder using a personal wallet did not lose tokens to this lending-pool withdrawal. A depositor who lent KAVA through Kava Lend has a claim against a pool that no longer holds enough tokens to meet those claims in full, based on Bitquery's November 14 snapshot. The difference matters much more than the headline dollar figure.
DefiLlama classified the November 14 event as an arithmetic error involving token and share accounting. It reported a loss estimate of $3.7 million, based on the tokens retained after repayments. This broadly matches the on-chain reconstruction, although the protocol team has not published its own final accounting.
Three questions remain open as of November 15:
Bitquery's reconstruction explains the observed transactions, but the team may revise the account of the software failure once its investigation is finished.
Mikko has been writing about money since 2015, covering payment services, trading platforms and crypto for readers in several markets. He leads exchange and wallet reviews at CryptoInfoBase.
Binance restored withdrawals on 87 networks after its $6.3 billion hack. Its November 14 update sets a new deadline, but some withdrawal routes remain closed.
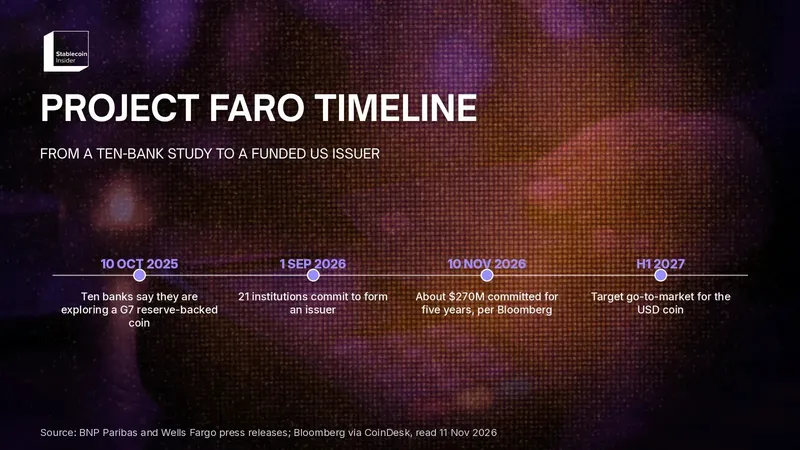
Goldman Sachs, Citi and 19 other financial firms back a reported $270M stablecoin venture. Project Faro targets a 2027 launch, with a euro token planned.
Deutsche Bank launched crypto custody on 11 November 2026 for corporate and institutional clients. It holds Bitcoin, Ether, USDC, EURC and EURAU.